Security model
Useful access, bounded deliberately.
WP Virtuoso is built around structured capabilities and human approvals rather than unrestricted server access.
Core boundaries
The dangerous shortcuts are intentionally missing.
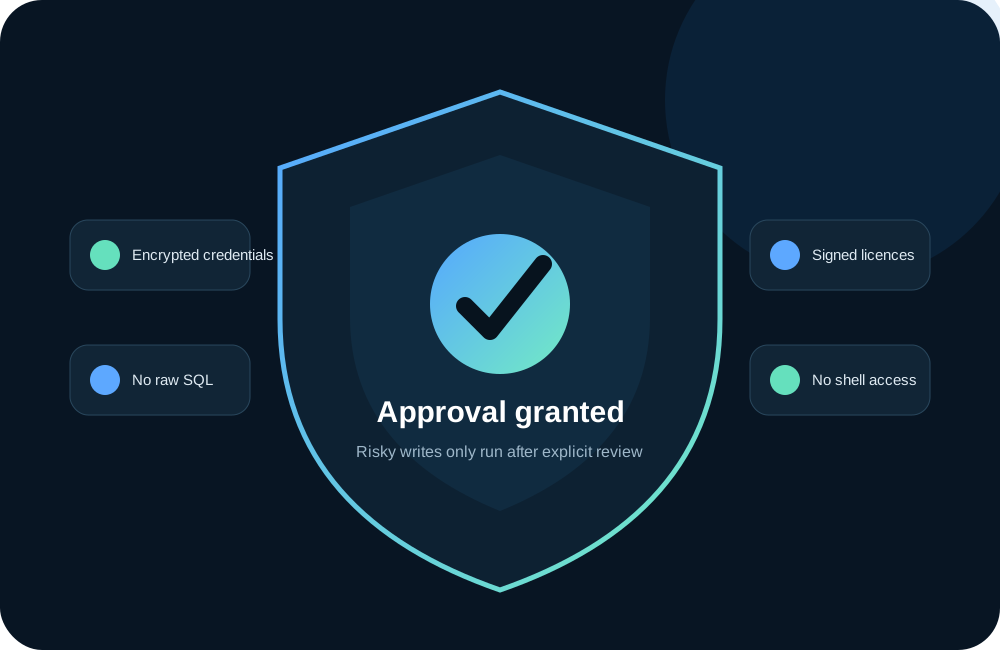
- No arbitrary shell execution exposed to AI clients
- No generic raw SQL execution
- No permanent-delete command surface
- WordPress capability checks still apply
- Application Passwords are revocable
- Controller credentials are encrypted at rest
- Commercial licences are signed and validated
- Approval payloads are bound to requested operations
Read-only first
Inspection and diagnostics can be separated from mutation privileges.
Explicit approvals
Guarded writes can stop for authorized review of the exact bound payload.
Recoverable work
Theme sandboxes, revisions, restore points, Trash and job receipts reduce risk.
Before general availability: publish a dedicated vulnerability-disclosure address and formal security response policy. During private testing, use the bug-reporting route in Support.